Admin Panel Security: Auth, CSRF, Sessions, Permissions
Securing an admin panel requires more than a login form. We break down practical approaches to authentication, CSRF protection, session management, and permissions based on years building production dashboards.
Every admin panel is a high-value target. It's the backstage pass to your application — customer data, configuration, revenue flows. At DigiForge we've built dozens of these for everything from custom CRM systems to multi-vendor marketplaces. And the one thing we've learned is that security can't be an afterthought. A single misstep in authentication, CSRF, sessions, or permissions can undo months of careful engineering. This article walks through the practical decisions we make in every project.
We're writing this because we've seen the same mistakes repeated: hardcoded tokens, session timeouts set to never expire, CSRF protection applied to half the endpoints. Each one is a ticking bomb. The goal here is to give you a framework for thinking about admin panel security — not just a checklist, but the reasoning behind the choices.
Authentication: More Than a Password Field
Authentication is the first gate. But too many implementations stop at a hashed password check. In our experience, a robust authentication layer includes these elements without exception:
- Password hashing using bcrypt, Argon2id, or scrypt — never SHA or MD5. We usually default to Argon2id if the framework supports it, as it's the most resistant to GPU-based attacks.
- Rate limiting on login endpoints to prevent brute force. A simple per-IP throttle with exponential backoff works wonders. We typically allow 5 attempts per minute, then double the wait window for each subsequent block.
- Account lockout after a configurable number of failed attempts (e.g., 5 attempts in 15 minutes). But allow administrators to unlock accounts via email or support ticket to avoid denial-of-service.
- Multi-factor authentication (MFA) for administrative accounts. Time-based one-time passwords (TOTP) are our standard recommendation. Push-based authentication via authenticator apps is also solid.
One pattern we see often — and strongly advise against — is rolling your own session token generation after login. Use the built-in session handling of your framework. If you're writing raw PHP, leverage password_hash and password_verify with the default algorithm. If you're in Laravel, use its built-in authentication scaffolding. The point is: don't reinvent cryptographic primitives.
Also, consider passwordless options like magic links or WebAuthn for admin users who struggle with password hygiene. But implement them as a second factor, not a replacement for passwords, unless you have a robust backup mechanism.
Cookie-based authentication sessions should always use the HttpOnly, Secure, and SameSite=Strict flags. Missing any of these is a common flaw we catch in security reviews. Additionally, set the cookie path to /admin or wherever your panel lives to limit exposure.
CSRF Protection: The Silent Vulnerability
Cross-Site Request Forgery (CSRF) allows an attacker to trick an authenticated admin into performing unintended actions — like deleting a user or changing a setting — by embedding a disguised request on a third-party site. Many developers assume it only matters for public-facing forms, but admin panels are especially attractive because their actions are privileged.
The standard defence is a CSRF token: a cryptographically random value bound to the session, included in every state-changing form or AJAX request. We always implement it using the framework's built-in CSRF protection. For a custom PHP implementation, it looks like this:
// Generating a CSRF token
$_SESSION['csrf_token'] = bin2hex(random_bytes(32));

// In the form:
echo '<input type="hidden" name="csrf_token" value="' . $_SESSION['csrf_token'] . '">';

// On submission:
if (!hash_equals($_SESSION['csrf_token'], $_POST['csrf_token'])) {
    die('CSRF token mismatch');
}
Key points: use hash_equals for comparison to prevent timing attacks, regenerate the token after the user logs in (or on every submission for extra safety), and never expose the token in GET requests. Also, remember to invalidate the token on logout. A stale token is an open door.
For AJAX-heavy admin interfaces, include the token in a custom header (e.g., X-CSRF-TOKEN) rather than in the URL. This prevents leakage via referrer headers. Some frameworks, like Laravel, automatically check for a token in the X-CSRF-TOKEN header if you set it with JavaScript.
In one engagement, we found an admin panel that only checked CSRF on POST requests but allowed state-changing GET parameters. That's a hard no. Every state change — PUT, DELETE, PATCH, even some GETs — should require a valid token. Also avoid using GET for any operation that modifies data.
Session Management: Don't Leave the Door Open
Sessions are the glue that keeps an authenticated user identified across requests. But poor session management is a common source of vulnerabilities. Here's what we treat as non-negotiable in every admin panel:
- Regenerate session ID after login and privilege escalation. Prevents session fixation attacks.
- Set a sensible session timeout. We configure idle timeouts (e.g., 30 minutes) and absolute timeouts (e.g., 12 hours) for sensitive panels. Absolute timeout forces re-authentication even if the user is active.
- Store sessions securely — use a fast, persistent store like Redis or a dedicated database table. Avoid file-based sessions on shared hosting, and never store sessions in a world-readable location.
- Implement session revocation. A 'logout everywhere' feature should invalidate all session records for that user, usually by incrementing a version field in the user record that is checked on each request.
One subtle but critical detail: bind the session to additional fingerprints like the user agent string or, more securely, a hash of the user's IP and the user agent. This way, if a session token is stolen, it cannot be used from a different browser or network. But be careful — overzealous IP binding can lock out legitimate users behind load balancers with changing IPs. We usually bind to a combination of user agent and a constant subnet (e.g., /24) derived from the IP.
Also consider session hijacking via XSS. Prevent XSS with proper output encoding and Content Security Policy headers. A single stored XSS can steal session cookies if they lack the HttpOnly flag. We always set cookies as HttpOnly, but a determined attacker can still make requests on behalf of the user via JavaScript if the CSRF token is accessible.
Always set the session cookie's SameSite attribute to Strict or Lax. In 2025, most browsers default to Lax, but we explicitly set it to Strict for admin panels to block cross-site requests entirely — except for top-level navigations.
Permissions: Granular Access Control
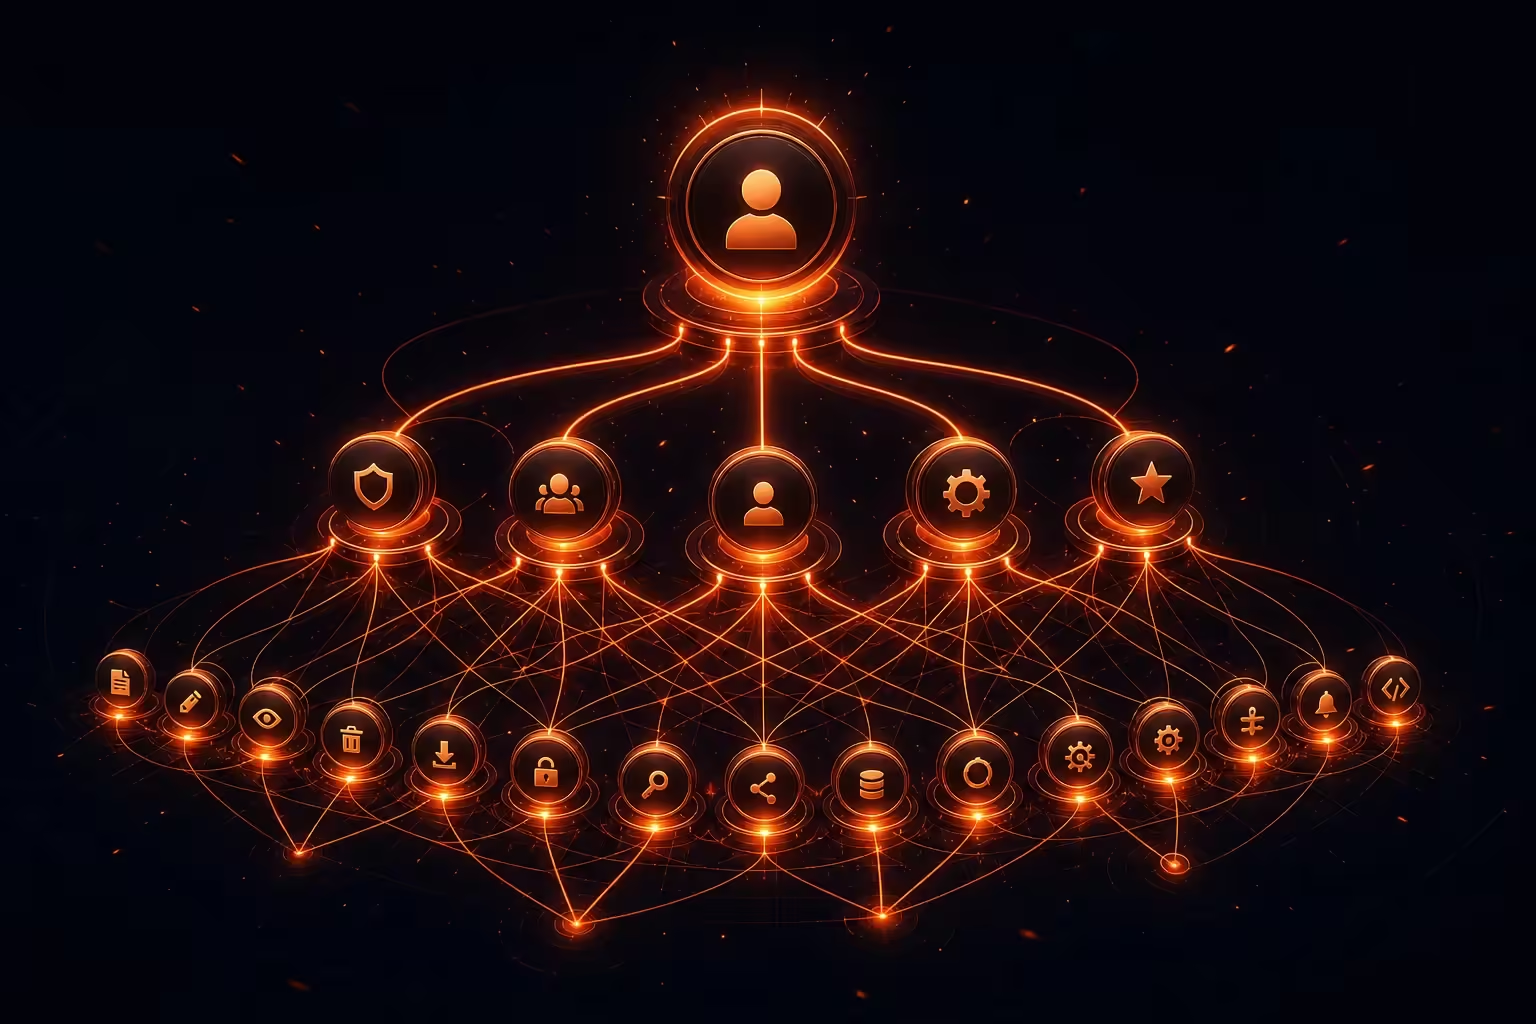
Once a user is authenticated and has a valid session, what can they actually do? Too many admin panels rely on a single 'superadmin' flag and nothing else. That's a recipe for internal threats and accidental damage. We always implement role-based access control (RBAC) with granular permissions.
RBAC means defining roles (e.g., 'editor', 'manager', 'admin') and assigning permissions to each role (e.g., 'view_users', 'edit_products', 'delete_orders'). A user then gets one or more roles. The check is typically done middleware-style: before any protected action, the system verifies the current user's roles include the required permission.
Key implementation practices we follow:
- Define permissions as a flat list of strings (e.g., 'users.create', 'users.delete'). Avoid numeric IDs that are hard to debug.
- Store role-permission mappings in the database, not in code, so you can update them without redeployment. But keep a cache layer (Redis) for performance.
- Cache permission lookups aggressively — a Redis set for 'user_id => [permissions]' is fast and easy to invalidate on role changes.
- Implement both 'allow' and 'deny' rules for edge cases, but keep the model simple. Overcomplicating permissions leads to bugs.
In custom builds at DigiForge, we often extend RBAC with attribute-based checks — for example, a manager can only edit orders assigned to their team. That's a business rule, not a pure permission, but it's enforced in the same authorization layer.
Also, audit permission changes. Log when an admin modifies roles or permissions, and who made the change. This is crucial for post-incident analysis.
Defense in Depth: Additional Layers
Authentication, CSRF, sessions, and permissions form the core, but they don't exist in isolation. We always add a few more layers to reduce risk:
- Content Security Policy (CSP): Restrict script sources to prevent XSS. A strict CSP like
default-src 'self'with nonces for inline scripts is best. - HTTP Strict Transport Security (HSTS): Enforce HTTPS. Admin panels should not be accessible over HTTP.
- X-Frame-Options: Set to
DENYto prevent clickjacking. - Audit logging: Log every admin action, especially sensitive ones like user deletion, payment modifications, or configuration changes. Store logs in an append-only system.
- IP whitelisting: For high-security panels, restrict access to known office IPs or VPN ranges.
None of these are silver bullets. A CSP bypass or a misconfigured proxy can undermine them. But together, they raise the bar significantly.
Putting It All Together
Securing an admin panel isn't about implementing any single feature perfectly — it's about the combination working together without gaps. Authentication must be strong and multi-layered. CSRF protection must be universal across all state-changing endpoints. Sessions must be bound, timed out, and revocable. Permissions must be granular and enforced at every entry point.
We've seen teams spend weeks building a beautiful dashboard only to leave the session cookie unsecured or forget to validate CSRF on an AJAX endpoint. The result: a theoretical takeover vector that could have been prevented with a few lines of configuration.
If you're building or maintaining an admin panel, do yourself a favour: audit these four areas with a critical eye. Use automated tools like OWASP ZAP or a simple checklist. And remember that security is a process, not a feature set. At DigiForge, we include a full security review in every custom build — from auth flow to permission edge cases. Because when it's your admin panel, every gate matters.
The best security is the one that's invisible to legitimate users but stops every attacker cold. That's the goal every time we start a new admin panel build.